TheStakk

Security and governance

Built for work that cannot live in a shared password manager.

TheStakk puts isolation, credential handling, permissions and execution history around every application and every workspace from the start.

Tenant isolation

EU region
Client A
Encrypted vault Own data Own team
Client B
Encrypted vault Own data Own team
Client C
Encrypted vault Own data Own team

no shared data · no shared credentials

One execution layer

Audit trail

Metered per workspace. Every run logged, exportable, attributable.

09:14 Client ASocial Content Manager logged
09:16 Client BMeeting Intelligence logged
09:21 Client CSocial Content Manager logged

Core controls

Security is part of the product architecture.

Not a layer added before procurement asks. These controls exist in every deployment, on both commercial routes.

7 controls · every workspace

01

Encrypted Vault

Client credentials encrypted at rest, never surfaced in logs or interfaces.

02

Tenant isolation

Strict separation of clients, data, inputs and results. Enforced at database level.

03

Role-based access

Control who can run apps, manage credentials and view results, per workspace.

04

Audit trail

Full execution history, per client, exportable.

05

GDPR & EU AI Act

Built for GDPR and the EU AI Act: data processing agreement, public subprocessor list, transparency on AI use.

06

Account security, the serious kind

Two-factor authentication (TOTP), active session management with remote sign-out, and a full trail of who did what, when, in every workspace.
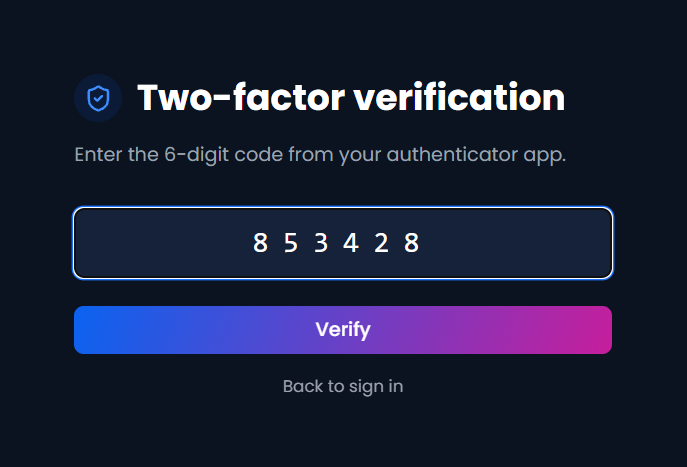
Two-factor verification screen: enter the 6-digit code from your authenticator app
07

Locked-down integrations

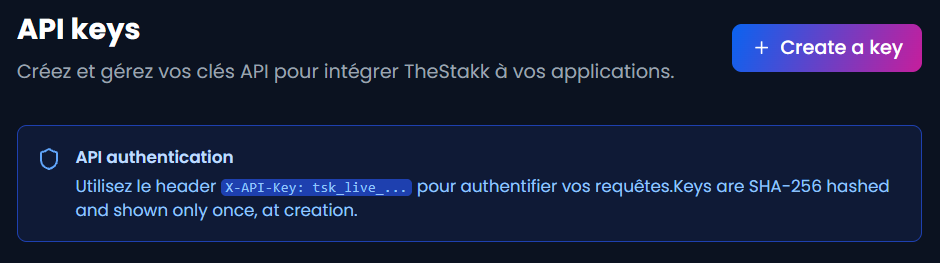
OAuth connections limited to the access strictly needed, API keys restricted per endpoint with IP allow-lists, per-key quotas, and one-click revocation. Third-party access is granted narrowly and revoked instantly.
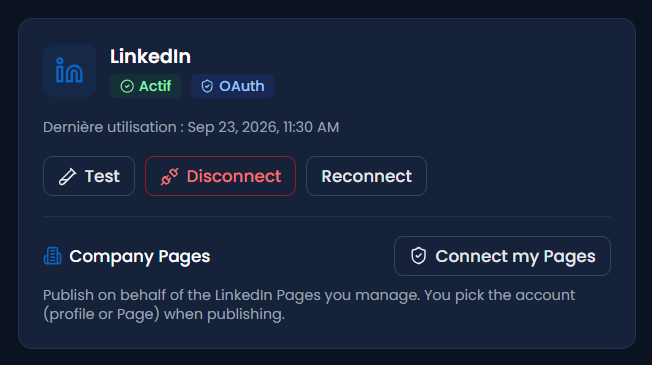
Connected LinkedIn account via OAuth, with test, disconnect and reconnect
API keys screen: keys SHA-256 hashed and shown only once, at creation

Data flow

What happens from connection to result.

01

Credentials enter the vault

Secrets are encrypted and kept outside application interfaces, results and execution logs.

02

Work runs inside its workspace

Inputs, data and results remain separated from every other customer or client tenant.

03

Every execution leaves a record

Authorised users can review and export run history without exposing internal application logic.

04

Customer data stays customer data

It is processed to produce the requested result. We never use your content to train any model. Our AI model providers do not use it for training either, under their terms for business use.

Published commitments

Clear answers before procurement asks.

Hosted in the European Union
Credentials encrypted in an isolated vault
Your workspace separated from every other customer
No training on your content, by us or our AI providers
Role-based access, controlled by you
Every run logged and exportable
Full list of subprocessors published
Data processing agreement↗ Privacy policy ↗

Choose how you use TheStakk

The controls stay consistent across every route.

Businesses receive them directly. Agencies extend them across every client workspace.